
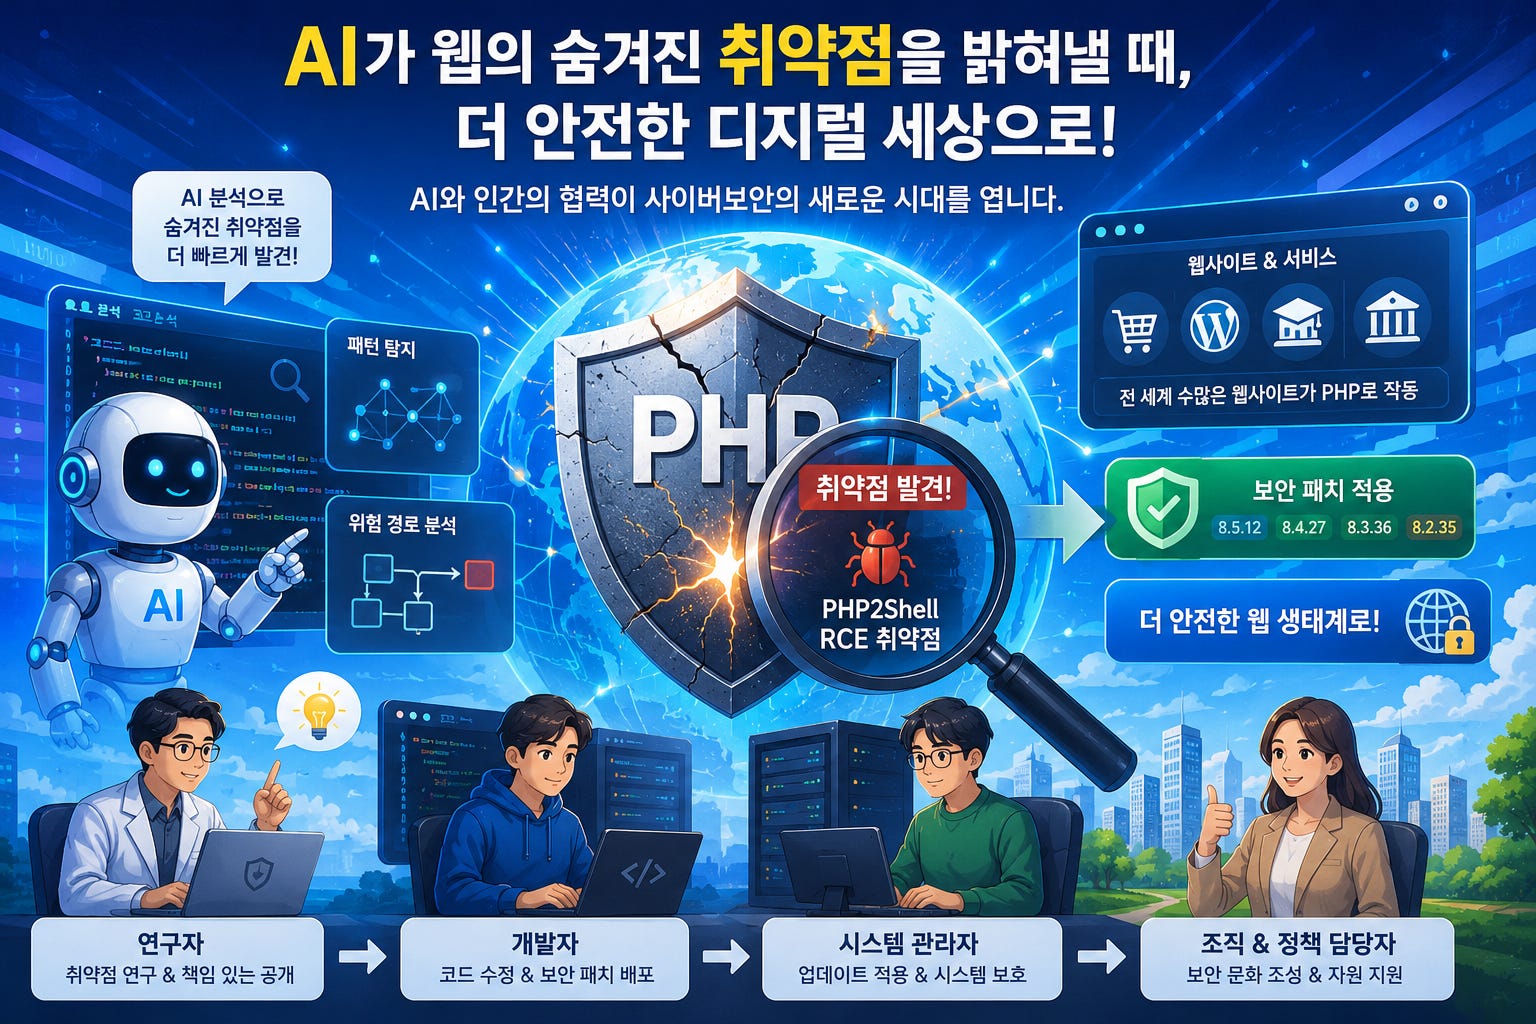
Image credit: Illustration generated with OpenAI’s ChatGPT image-generation tool, 2026.
When AI Uncovers the Web’s Hidden Fault Lines: Cybersecurity at the Threshold of a New Era
Abstract
The discovery of critical PHP vulnerabilities in October 2026 offers a compelling illustration of how artificial intelligence (AI) is reshaping cybersecurity research and the protection of digital infrastructure. PHP remains one of the most widely used server-side programming languages, making vulnerabilities in its ecosystem a matter of considerable concern. Wiz Research reported that AI-assisted analysis contributed to the identification of critical vulnerabilities capable of enabling unauthenticated remote code execution under affected conditions. In response, the PHP development team released security updates and urged users to upgrade supported versions. Subsequent news coverage reflected growing concern among organizations and public authorities. Nevertheless, the prevalence of PHP must not be conflated with the proportion of websites that are vulnerable or compromised. This essay examines the reported PHP2Shell vulnerabilities, the emerging role of AI in security research, the limits of the available evidence, and the responsibilities of software developers, system administrators, organizational leaders, and policymakers. It argues that AI can substantially strengthen cybersecurity, but its promise can be realized only through rigorous verification, responsible disclosure, timely remediation, and sustained human oversight.
Keywords: artificial intelligence, cybersecurity, PHP2Shell, remote code execution, vulnerability discovery, responsible disclosure, software security, AI governance
The Hidden Fault Lines Beneath the Web
The internet presents itself as a remarkably seamless world. With a few clicks, we read the news, conduct business, exchange ideas, and communicate across continents. Beneath this apparent simplicity, however, lies an intricate infrastructure of programming languages, software libraries, databases, servers, and communication protocols. Most of the time, these components perform their duties quietly and invisibly. We tend to notice them only when something goes wrong.
PHP has long been one of the principal building blocks of the modern web. It supports a vast ecosystem of websites and applications, including installations of WordPress, Drupal, and Joomla. Its accessibility, mature development environment, and extensive community have helped make it a durable choice for server-side programming. Yet longevity has a paradoxical side. Software that remains useful for decades may also accumulate layers of complexity, inherited assumptions, and interactions that are difficult to scrutinize comprehensively.
In October 2026, Wiz Research announced the discovery of critical PHP vulnerabilities that could permit unauthenticated remote code execution under affected conditions. The researchers presented their findings under the name PHP2Shell, drawing attention to the potential consequences of weaknesses in software that underpins a substantial portion of the web (Tzadik et al., 2026).
The significance of the discovery extends beyond the vulnerabilities themselves. It lies in the convergence of three developments: the extensive adoption of PHP, the potentially severe consequences of the reported flaws, and the growing capacity of AI-assisted tools to help researchers uncover weaknesses in complex software systems.
When a widely used component proves vulnerable, the implications can extend well beyond the organization that maintains it. Businesses, educational institutions, public agencies, and individual website operators may all need to determine whether their systems are affected. Yet broad adoption does not establish universal exposure. Actual risk depends on the software version, system configuration, application behavior, network accessibility, and other conditions that determine whether a particular attack path is viable.
Precision matters. A vulnerability affecting widely deployed software warrants urgent attention, but urgency should be guided by evidence rather than inflated by assumption.
When Artificial Intelligence Joins the Hunt
Traditional vulnerability research demands a formidable combination of skills. Researchers must understand software architecture, trace the movement of untrusted input, examine boundary conditions, and investigate how seemingly harmless components may interact in unexpected ways. A vulnerability may remain concealed not because its underlying logic is incomprehensible, but because recognizing its significance requires connecting details scattered throughout a large and complicated codebase.
AI is beginning to change this investigative process.
Modern AI systems can assist researchers in navigating unfamiliar code, identifying suspicious patterns, generating test hypotheses, and examining interactions that deserve closer scrutiny. They can help summarize complex execution paths, suggest alternative explanations, and accelerate the exploration of potential weaknesses. Used judiciously, these capabilities can expand the range of investigations a researcher can undertake within a limited amount of time.
The PHP2Shell report illustrates this emerging role. Wiz Research described how AI-assisted analysis contributed to its investigation of PHP and the identification of vulnerabilities with serious security implications (Tzadik et al., 2026).
The important point is not that AI has suddenly become an infallible security expert. Rather, it can help researchers ask better questions, explore more possibilities, and recognize relationships that might otherwise escape notice. A model may identify an unusual pattern or suggest a promising experiment; a researcher must still determine whether the hypothesis withstands testing and whether the resulting finding has practical security significance.
This distinction separates discovery from proof. An AI-generated explanation is not, by itself, evidence that a vulnerability exists. A plausible exploit is not proof that every installation can be compromised. Nor does a successful demonstration in a controlled environment establish that the same attack will work against every production system.
Credible vulnerability research therefore requires reproducibility, technical validation, careful documentation, and responsible communication with the relevant software maintainers. AI may accelerate the search, but evidence must determine the result.
The broader lesson is that AI is becoming a powerful research partner—not a substitute for professional judgment. Its value lies in helping human investigators see more, test more, and reason more efficiently without surrendering the obligation to verify what they discover.
Understanding the PHP2Shell Vulnerabilities
On October 21, 2026, the PHP development team published a security advisory describing critical remote code execution vulnerabilities and urging users to update affected installations. The advisory identified patched releases in four supported branches: PHP 8.5.12, 8.4.27, 8.3.36, and 8.2.35 (PHP Development Team, 2026a).
Remote code execution is particularly serious because it can allow an attacker to cause a target system to execute code under specific conditions. Depending on the affected application, the privileges available to the compromised process, and the surrounding security controls, successful exploitation may expose sensitive information, disrupt services, or provide a foothold for further malicious activity.
The term unauthenticated remote code execution carries additional significance. It indicates that the relevant attack path may be reachable without first authenticating through the affected application. It does not mean, however, that every server is accessible to an attacker or that exploitation will succeed regardless of configuration. Network exposure, software versions, application behavior, and other environmental conditions remain critical.
The official PHP advisory provides the practical foundation for responding to the discovery. Security researchers can identify a weakness and demonstrate its implications, but software maintainers must investigate the problem, develop appropriate fixes, and distribute them through trusted release channels. Organizations must then determine which of their systems are affected and implement the necessary remediation.
Cybersecurity, in this sense, is a chain of shared responsibilities. Researchers identify and disclose weaknesses; maintainers develop and publish fixes; developers update their applications and dependencies; administrators deploy and verify the changes; and organizational leaders ensure that the process receives sufficient attention and resources.
The PHP project’s support policy adds another complication. PHP 8.1 and earlier no longer receive updates from the PHP project, although some third-party long-term-support providers may supply backported fixes. Organizations operating older installations must therefore establish whether their particular support arrangements include an appropriate security fix. An unsupported system cannot be assumed to receive the same protection as a currently supported release.
The official archive also included an informational advisory on October 23, 2026, concerning session upload progress. It described a further remote-code-execution possibility dependent on an unusual combination of configuration settings and application code, and recommended disabling session upload progress as an interim precaution pending a subsequent regular bug-fix release (PHP Development Team, 2026b).
This subsequent advisory illustrates an essential principle of security management: an initial announcement may not be the final word. As investigations continue, maintainers may clarify attack conditions, identify additional risks, or refine recommended mitigations. Responsible administrators must therefore monitor official advisories and release notes rather than treating the first announcement as a complete and permanent account of the problem.
Evidence, Interpretation, and the Limits of Certainty
The public discussion of PHP2Shell demonstrates how easily distinct technical claims can become blurred when a complex security issue enters the news cycle.
The first claim concerns PHP’s prevalence. Wiz Research emphasized the language’s extensive use across the web. That prevalence explains why a serious PHP vulnerability deserves broad attention. It does not establish that an equivalent proportion of websites is vulnerable, exposed, or compromised.
The second claim concerns the vulnerabilities themselves. The researchers reported critical weaknesses and described their potential consequences. These findings constitute substantive technical evidence, but their implications must be understood within the scope of the research, the affected software, and the conditions necessary for exploitation.
The third claim concerns real-world attacks. Public disclosure can prompt defensive scanning and patching, while also giving malicious actors information they may use to investigate potential attack paths. Nevertheless, the possibility of exploitation is not the same as proof that a particular organization has suffered a successful attack.
The fourth claim concerns demonstrations. A controlled test can establish that a vulnerability is exploitable under specified conditions. It cannot automatically establish that the same conditions exist across every deployment of the software.
These distinctions are not academic niceties. They are the foundation of sound risk assessment. Exaggerating a threat can generate unnecessary alarm, misdirect scarce resources, and erode public confidence. Minimizing a serious vulnerability can leave systems exposed. Responsible communication must resist both temptations.
A disciplined assessment asks what kind of evidence supports each conclusion. Official advisories establish what maintainers have announced and which fixes they recommend. Technical reports describe researchers’ findings and methods. Independent testing can strengthen confidence in the reported results. Incident investigations and forensic evidence are necessary to substantiate claims about actual compromise.
The quality of a security decision depends not only on the amount of information available, but also on whether that information is interpreted within its proper evidentiary limits. In cybersecurity, intellectual restraint is not a sign of indecision. It is a form of professional rigor.
The Race Between Disclosure and Exploitation
Once a critical vulnerability becomes public, the time available for an orderly response may narrow considerably. Organizations must determine whether they are affected, identify exposed systems, obtain and test fixes, and deploy updates without unnecessarily disrupting essential services.
Malicious actors may simultaneously examine the public information in search of opportunities. The result is a familiar asymmetry: defenders must understand and remediate their exposure across complicated environments, while attackers may need only one viable path into one inadequately protected system.
News coverage published on October 23, 2026, described heightened concern following the PHP disclosures, including precautionary actions by some organizations and increased attention from public authorities (Jeon et al., 2026). Such reporting provides context for the broader response, but precautionary shutdowns and heightened alerts should not be interpreted automatically as evidence of confirmed PHP2Shell exploitation.
For administrators, the first task is visibility. An organization cannot protect assets it does not know exist. PHP may be present across production servers, cloud workloads, virtual machines, container images, third-party applications, and legacy systems maintained by different teams. An incomplete inventory can leave precisely the systems most in need of attention outside the remediation process.
The next task is verification. Administrators should establish which versions are installed, consult the official advisory, and determine whether the relevant attack conditions apply. Updates should be obtained from trusted sources, tested as appropriate, and deployed according to the organization’s exposure and operational requirements.
Where immediate updating is not feasible, administrators may need to implement temporary mitigations consistent with the official guidance and increase monitoring. Such measures should be treated as interim risk reduction, not as a permanent replacement for a supported fix when one is available.
Organizations should also examine relevant logs and security telemetry for indications of suspicious activity. Monitoring can support the detection and investigation of possible attacks, although the absence of obvious alerts does not establish that a system is uncompromised.
The objective is not simply to move faster than the attacker. It is to make informed decisions quickly, reduce exposure systematically, and verify that remediation has actually succeeded.
Why a Software Flaw Becomes a Public Concern
A vulnerability in a programming language or shared software component can affect far more than the developers responsible for maintaining it. Websites now support essential activities in commerce, education, healthcare administration, public communication, and government services. When a common component is at risk, the potential consequences can cross institutional and national boundaries.
Software dependencies make the problem more complicated. An organization may rely on a content-management system or third-party application without having written the underlying code. A hosting provider may control part of the infrastructure, while an external vendor manages another component. Each participant may have different responsibilities, access privileges, and update schedules.
This fragmented environment complicates accountability. Software maintainers must investigate reported weaknesses and provide appropriate fixes. Application developers must use components safely and keep dependencies current. Hosting providers must maintain their infrastructure and communicate relevant risks. Organizations must inventory their assets, assess their exposure, and act on security guidance. Executives must ensure that cybersecurity is supported by adequate staffing, authority, and investment.
No single participant can eliminate every vulnerability. Yet each can reduce the likelihood that a known weakness develops into a serious incident.
The responsibility of individual users is more limited. People can practice good account security and keep their own devices updated, but they cannot reasonably be expected to inspect the source code of every website they visit. The primary responsibility for securing internet-facing infrastructure belongs to the organizations that operate it and the vendors that develop and maintain its components.
Cybersecurity is therefore not merely a technical discipline. It is an institutional commitment to reliability, accountability, and public trust.
AI as Both a Defensive Advantage and a Source of Risk
The capabilities that make AI useful for discovering vulnerabilities can also strengthen defensive operations. AI-assisted tools can help security teams analyze code, summarize alerts, prioritize remediation, investigate anomalous behavior, and identify potentially unsafe programming patterns. They may also help developers examine proposed changes before those changes enter production.
These benefits, however, are not guaranteed. AI systems can produce false positives, overlook important conditions, misinterpret code, or recommend changes that introduce new defects. A confident explanation is not necessarily a correct explanation, and an automated security assessment should never be accepted uncritically merely because it was generated quickly.
AI also presents a dual-use challenge. Knowledge that enables defenders to understand an attack path may help malicious actors reproduce it. Public technical reports can strengthen collective security by allowing researchers and vendors to validate findings, develop fixes, and improve detection. At the same time, some disclosures can reduce the effort required to adapt an attack technique.
The appropriate response is neither to reject AI-assisted security research nor to release technical information without regard for its consequences. It is to combine timely disclosure with responsible coordination, rigorous validation, clear mitigation guidance, and careful communication.
Organizations introducing AI into security operations must exercise comparable discipline. They should establish rules for handling sensitive data, restrict unnecessary access to production systems, require human approval for consequential actions, and independently validate automated findings. AI should enhance the quality of security decisions, not become a convenient excuse for transferring accountability to a machine.
Intelligent security requires more than intelligent software. It requires institutions capable of using that software responsibly.
From Reactive Patching to Continuous Resilience
The PHP2Shell episode reinforces a lesson that predates AI: cybersecurity cannot depend exclusively on reacting after a vulnerability becomes public.
Resilient organizations maintain an ongoing process for discovering assets, tracking dependencies, evaluating exposure, applying security updates, and confirming that remediation has worked. This process must include less visible systems—old virtual machines, test environments, abandoned applications, and container images that remain embedded in deployment pipelines.
Software bills of materials can help organizations understand which components are included in their applications. Vulnerability-management platforms can correlate inventories with published advisories. Configuration management can promote consistent security settings, while logging and monitoring can provide evidence of suspicious activity. These technologies are most effective when their outputs lead to clearly assigned responsibilities and measurable remediation actions.
AI may help organizations manage the resulting workload. It could summarize which assets appear to contain an affected component, highlight gaps in inventory data, or group related alerts for investigation. Yet its conclusions must remain traceable to reliable data and verifiable methods. An automated statement that a system is safe is not a substitute for evidence that the relevant vulnerability has been addressed.
Resilience also depends on preparation. Incident-response exercises allow teams to rehearse technical investigation, executive communication, vendor coordination, and service recovery. Backup and restoration procedures must be tested rather than merely documented. Organizations supporting essential services should plan for the possibility that emergency updates or containment measures may temporarily disrupt normal operations.
Mature cybersecurity is not defined by an unrealistic promise that vulnerabilities will never occur. It is defined by the capacity to discover weaknesses, evaluate their significance, respond effectively, and improve the process after each incident.
The Human Judgment Behind Intelligent Security
As AI becomes increasingly capable of identifying software weaknesses, an important question arises: what remains distinctively human in cybersecurity?
The answer begins with judgment and responsibility. AI can suggest a vulnerability, but people must determine how to validate the finding, disclose it responsibly, prioritize remediation, and balance technical risk against operational needs. Such decisions require expertise, ethical reasoning, institutional knowledge, and an understanding of consequences that extend beyond a line of code.
Researchers must distinguish confirmed findings from promising hypotheses. Maintainers must communicate fixes accurately. Administrators must verify that updates have been installed and that the intended protection is in place. Organizational leaders must provide the resources and authority needed to act. Policymakers must encourage cooperation and responsible disclosure while distinguishing credible warnings from unsupported claims.
Education is equally important. Future cybersecurity professionals must learn not only how to use AI tools but also how to interrogate their outputs. They need to test assumptions, preserve evidence, document uncertainty, and explain technical risks in language that decision-makers can understand. The ability to ask a model for an answer is not equivalent to the ability to evaluate that answer.
A powerful AI system can accelerate an investigation, but acceleration without judgment may merely produce mistakes more efficiently. The goal should be a partnership in which machine-assisted analysis expands human capability while people remain accountable for the decisions that affect systems, institutions, and lives.
Toward a More Resilient Digital Civilization
The PHP2Shell discovery marks a consequential moment in the evolving relationship between AI and cybersecurity. It demonstrates the potential of AI-assisted vulnerability research and underscores the importance of coordinated action when serious weaknesses emerge in widely deployed software.
It does not prove that every PHP-based website is vulnerable, that AI can identify every security weakness, or that an automated analysis can reliably certify a system as safe. Those conclusions would exceed the available evidence. What the episode does demonstrate is that the speed and reach of vulnerability research are changing, while the fundamental obligations of software maintenance, verification, and responsible disclosure remain.
The future of cybersecurity will depend on more than increasingly sophisticated models. It will require reliable evidence, secure development practices, accurate asset inventories, timely updates, transparent communication, independent verification, and people prepared to exercise sound judgment under pressure.
The internet is sustained by countless components that remain invisible to most of its users. Its reliability depends on how carefully those components are designed, maintained, and repaired. AI may enable us to uncover hidden weaknesses earlier and investigate them more efficiently. Whether that capability makes the digital world safer will depend on how wisely we respond to what it reveals.
Ultimately, the measure of intelligent security is not how many vulnerabilities a machine can discover. It is whether human beings and the institutions they build can transform that knowledge into meaningful protection, enduring resilience, and public trust.
References
Jeon, H., Kwak, D., & Yoon, D. (2026, October 23). 세계 웹사이트 70%에 보안 구멍 ‘버그마겟돈 비상’ [Security vulnerabilities in 70% of the world’s websites: Bugmageddon alert]. Dong-A Ilbo. https://www.donga.com/news/Inter/article/all/20261023/134893713/2
PHP Development Team. (2026a, October 21). Security advisory: Critical remote code execution vulnerabilities, update now. PHP.net. https://www.php.net/archive/2026.php#2026-10-21-5
PHP Development Team. (2026b, October 23). Informational advisory: Session upload progress. PHP.net. https://www.php.net/archive/2026.php
Tzadik, S., Tamari, S., Ohfeld, N., & Schwartz, T. (2026, October 21). PHP2Shell: AI uncovers critical RCE vulnerabilities affecting 70% of the Internet. Wiz Research. https://www.wiz.io/blog/php2shell-php-rce
AI가 웹의 숨겨진 취약점을 발견할 때: 새로운 시대의 문턱에 선 사이버보안
치명적인 PHP 보안 취약점의 발견
한글 요약
2026년 10월 공개된 PHP2Shell 취약점 사례는 인공지능(AI)이 사이버보안 연구와 디지털 인프라 보호에 어떤 변화를 가져오고 있는지 보여준다. PHP는 전 세계 웹 환경에서 널리 사용되는 서버 측 프로그래밍 언어로, 관련 취약점의 발견은 웹사이트 운영자와 기업, 공공기관에 중요한 보안 과제를 제기한다. Wiz Research는 AI를 활용한 분석이 인증되지 않은 원격 코드 실행을 가능하게 할 수 있는 중대한 PHP 취약점의 발견에 기여했다고 발표했으며, PHP 개발팀은 보안 패치를 배포하고 지원되는 버전으로 업데이트할 것을 권고했다.
이번 사례의 핵심은 AI가 복잡한 소프트웨어의 취약점을 찾아내는 연구 과정을 가속할 수 있다는 점이다. AI는 코드 분석, 의심스러운 실행 경로 탐색, 테스트 가설 생성 등을 지원함으로써 연구자의 분석 능력을 확장할 수 있다. 그러나 AI가 제시한 결과가 곧 검증된 사실을 의미하지는 않는다. 취약점의 실제 영향과 악용 가능성을 판단하려면 재현 가능한 시험, 기술적 검증, 독립적인 평가가 필요하다.
또한 PHP가 널리 사용된다는 사실과 전체 웹사이트의 70%가 취약하거나 침해되었다는 주장은 엄격히 구분해야 한다. 실제 위험은 소프트웨어 버전, 시스템 구성, 애플리케이션의 동작, 네트워크 접근성 및 패치 적용 여부 등에 따라 달라진다. 따라서 보안 대응은 과장된 위협 인식이나 근거 없는 낙관론이 아니라 정확한 증거와 공식 보안 권고에 기초해야 한다.
이 글은 사이버보안이 단순히 취약점을 발견하는 기술적 활동을 넘어 공동의 책임을 요구하는 사회적 과제임을 강조한다. 연구자는 책임 있게 취약점을 공개하고, 소프트웨어 개발자는 신속하게 수정 사항을 제공하며, 시스템 관리자는 자산을 파악하고 패치를 적용한 뒤 그 효과를 확인해야 한다. 조직의 지도자와 정책 담당자 역시 적절한 자원과 협력 체계를 마련해야 한다.
결론적으로 AI는 사이버보안을 강화하는 강력한 도구가 될 수 있지만, 그 효과는 인간의 판단력과 책임 있는 활용에 달려 있다. 디지털 사회의 안전은 기계가 얼마나 많은 취약점을 발견하는가만으로 결정되지 않는다. 발견된 지식을 실제 보호 조치로 전환하고, 지속적인 보안 관리와 독립적인 검증을 통해 디지털 인프라의 회복탄력성과 사회적 신뢰를 확보하는 능력이 더욱 중요하다.
핵심어
인공지능, 사이버보안, PHP2Shell, 원격 코드 실행, 취약점 탐지, 책임 있는 취약점 공개, 소프트웨어 보안, 보안 패치, AI 거버넌스, 디지털 인프라 회복탄력성
About the Author

Prof. Dr. Young Choi (Editor-in-Chief) — Regent University
Full list of his K-GSP columns
Full list of his Books at Amazon.com
Young B. Choi is a Professor in the Department of Engineering & Computer Science at Regent University. He published 38 books with ‘Selected Readings in Cybersecurity’ (2018) (about 800 copies archived globally at university/college libraries around the world) and ‘Cybersecurity Applications and Artificial Intelligence’ (2023) available in seven major world languages. He proposed the world’s first global and universal telecommunications “Service Order Handling (SOH)” Model (T-SOH Model) (1995) with Dr. Adrian Tang. With this innovative research work, he received the IEEE NOMS ’96 Best Paper Award and became the first recipient of the Outstanding Contribution Award of the TeleManagement Forum in 1998. His research areas include Natural Language Processing-focused AI, AI-applied cybersecurity, network and telecom service management, and Korean studies on Gani Choi Rip’s Jeonggwan (靜觀: Quiet Contemplation) philosophy and Shilhak ( 實學: Practical Learning).
Suggested Citation
Choi, Y. B. (2026). When AI Uncovers the Web’s Hidden Fault Lines: Cybersecurity at the Threshold of a New Era. K-GSP Forum.
© K-Global Scholars and Professionals Forum. All rights reserved. 2026. Content published in the K-GSP Forum may not be reproduced, distributed, or transmitted in any form without prior written permission from the K-GSP Forum, except for brief quotations with full attribution.